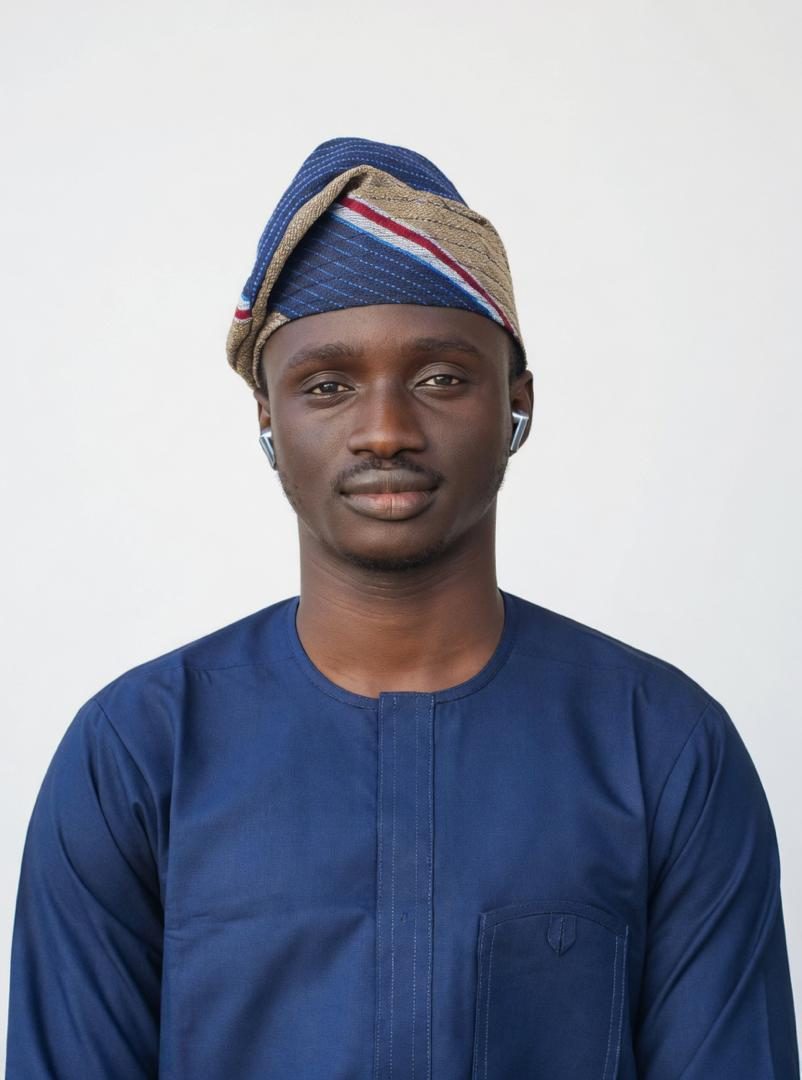
01 Who I am
Health research taught me rigour. Security taught me paranoia. Engineering is where both get used.
02 Ask the site
A real shell. Type help, or just poke at it. It answers with everything on this page.
03 What I do
Six disciplines that keep feeding each other. Tap any row for detail.
04 The Tool Lab
Twenty working tools, not screenshots. Everything executes locally in your browser, no server, no telemetry, nothing you type leaves this machine.
| Attacker | Hardware | Guesses/sec | Time to break |
|---|
Paste a raw HTTP response header block (from curl -I or DevTools → Network → Headers).
Graded against OWASP Secure Headers guidance.
| # | Network | First host | Last host | Broadcast | Hosts |
|---|
A safe demonstration of why unsanitised input is dangerous. The "vulnerable" render below uses
innerHTML inside a sandboxed frame; the hardened one escapes and CSP-restricts it.
Nothing executes against this page.
◉ Vulnerable render, innerHTML
◉ Hardened render, escaped + CSP
Load a dataset first.
Pearson correlation across every numeric field. Deep teal = positive, deep rust = negative.
A tiny SQL engine over your loaded table (aliased data).
Supports SELECT … FROM data WHERE … ORDER BY … LIMIT …, plus
COUNT/SUM/AVG/MIN/MAX and GROUP BY.
Distribution
Box plot
Welch's two-sample t-test, no equal-variance assumption.
Cochran's formula with finite-population correction, the calculation I reach for in research design.
A real fetch client. Cross-origin requests obey the target's CORS policy, a blocked request is the browser's security model working, and the response panel explains which one fired.
Generated with crypto.getRandomValues(), a CSPRNG, not Math.random().
05 Selected work
Things I built end to end. The first three are running on this page right now.
06 Flagship builds
The serious projects. Not live toys, real systems. Request a private walkthrough of any of them.
07 Credentials
Every one verifiable at source. Click any card to read the certificate.
08 The path here
Research ethics to offensive security, roughly in that order.
09 Beyond the code
I do not just build the tech. I help run the company behind it.
10 Get in touch
Let's build
something
that holds.
Security review, a Python tool that saves your team a week, a full build from scratch, or just to argue about whether that CVE is actually exploitable. I reply to everything.
Request freelance work